NetSuite SuiteScript Requests Blocked? Use an Inbound Proxy for a Static Source IP
A NetSuite SuiteScript integration can make a valid HTTPS request and still receive a security challenge instead of the API response it needs. If the destination is filtering NetSuite’s shared source IPs, changing the request body or credentials will not address the network-level problem.
For a SuiteScript integration calling a WordPress REST endpoint, a QuotaGuard Inbound Proxy provides a practical alternative: send the request to a normal HTTPS hostname on port 443, and let the proxy forward it to the destination from your subscription’s static IPs. You do not need to configure a forward proxy inside SuiteScript.
We recently helped a customer get this working after their NetSuite-to-WordPress integration encountered a hosting provider’s security filters. Here is what happened, why the initial proxy approach failed, and how to use the working pattern.
When Shared Source IPs Trigger a Security Challenge
The customer’s Suitelet sent HTTPS POST requests to a WordPress REST endpoint on SiteGround. SiteGround’s explanation, relayed by the customer, identified a network-level reputation problem: automated security filters had flagged the shared source subnet because another system within that range was making high-frequency login attempts.
Those filters operated at the web server and proxy layer, before the request reached PHP or WordPress. The integration was encountering a verification challenge rather than reaching the application normally.
The customer suspected that a NetSuite data-center move had placed their account on the affected subnet. They also noted that a SiteGround change could have happened around the same time. We could not establish which change triggered the incident, but the host’s explanation identified why requests from that source range were being challenged.
That distinction matters when troubleshooting. A destination may reject a request because its source is missing from an allowlist, or it may challenge it because of an IP-reputation rule. Those are different controls. Ask the destination operator which one is responsible before changing application code or adding addresses to an allowlist.
Why NetSuite’s Outbound Addresses Are Not a Fixed Identity
Oracle’s NetSuite IP-address guidance says addresses can change without notice. Its outbound-access guidance also explains that support does not provide a list of outbound addresses and that customers relying on IP-based firewall rules must maintain them as ranges change.
Oracle documents an option for advanced firewalls: resolve outboundips.netsuite.com and automatically grant access to requests from the resulting addresses. That can be useful when the destination supports DNS-based rules and wants to accept NetSuite’s outbound traffic.
It does not give your particular integration an exclusive address, however. Nor does a DNS-based allowlist automatically override a hosting provider’s separate reputation filters.
A proxy provides another route. The destination sees the proxy’s source IPs rather than the original NetSuite addresses, so the integration’s source identity is no longer tied to where NetSuite runs the account.
Why Posting Directly to the Forward Proxy Did Not Work
The customer initially tried sending an HTTPS request to QuotaGuard’s forward-proxy hostname on port 9293, adding a Host header for the WordPress site and a Proxy-Authorization header.
That is not equivalent to configuring an HTTP client to use a forward proxy.
QuotaGuard Static’s port 9293 is an HTTP forward-proxy endpoint, not an ordinary HTTPS API endpoint. A proxy-capable client knows how to establish the appropriate proxy connection to the destination. Simply replacing the destination hostname with the proxy hostname does not make a normal HTTPS POST behave that way.
SuiteScript’s N/https module does not expose a forward-proxy setting in its documented request API. Oracle also explicitly lists Host among the headers whose manually supplied values are discarded. Setting it in script therefore cannot redirect that request to the intended website.
The customer additionally reported an outbound HTTPS port restriction to 443 or 8443. We have not verified that as a universal NetSuite restriction. It was another constraint in this case, but switching the forward proxy’s port would not have solved the missing proxy-client support.
The Working Pattern: An Inbound Proxy on Port 443
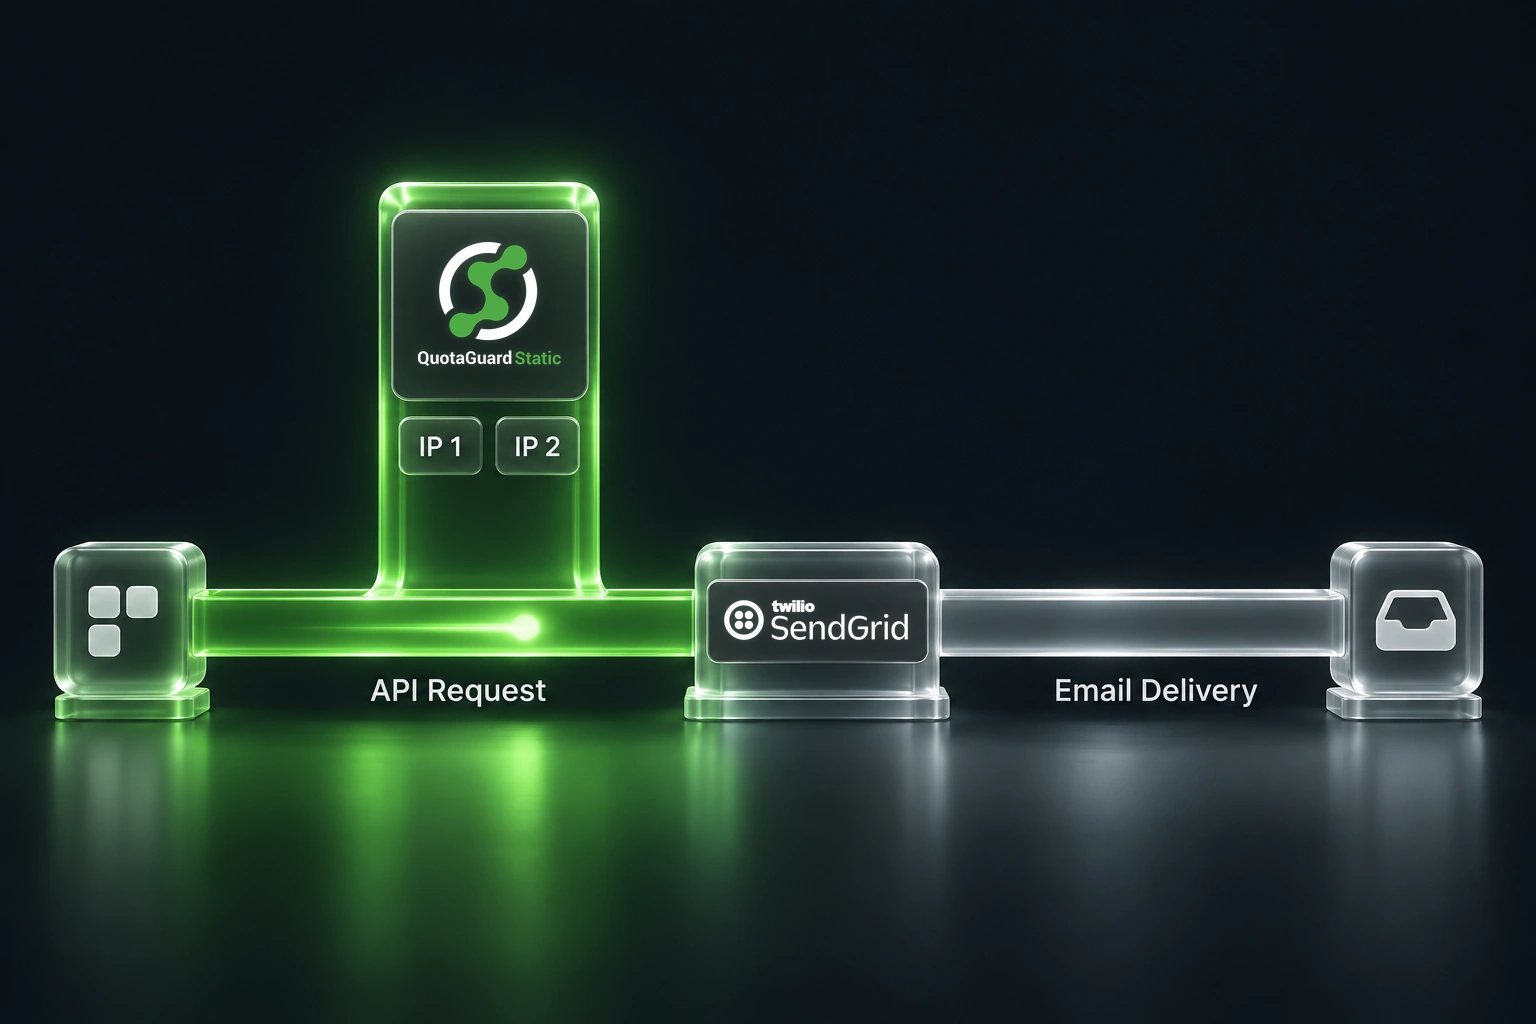
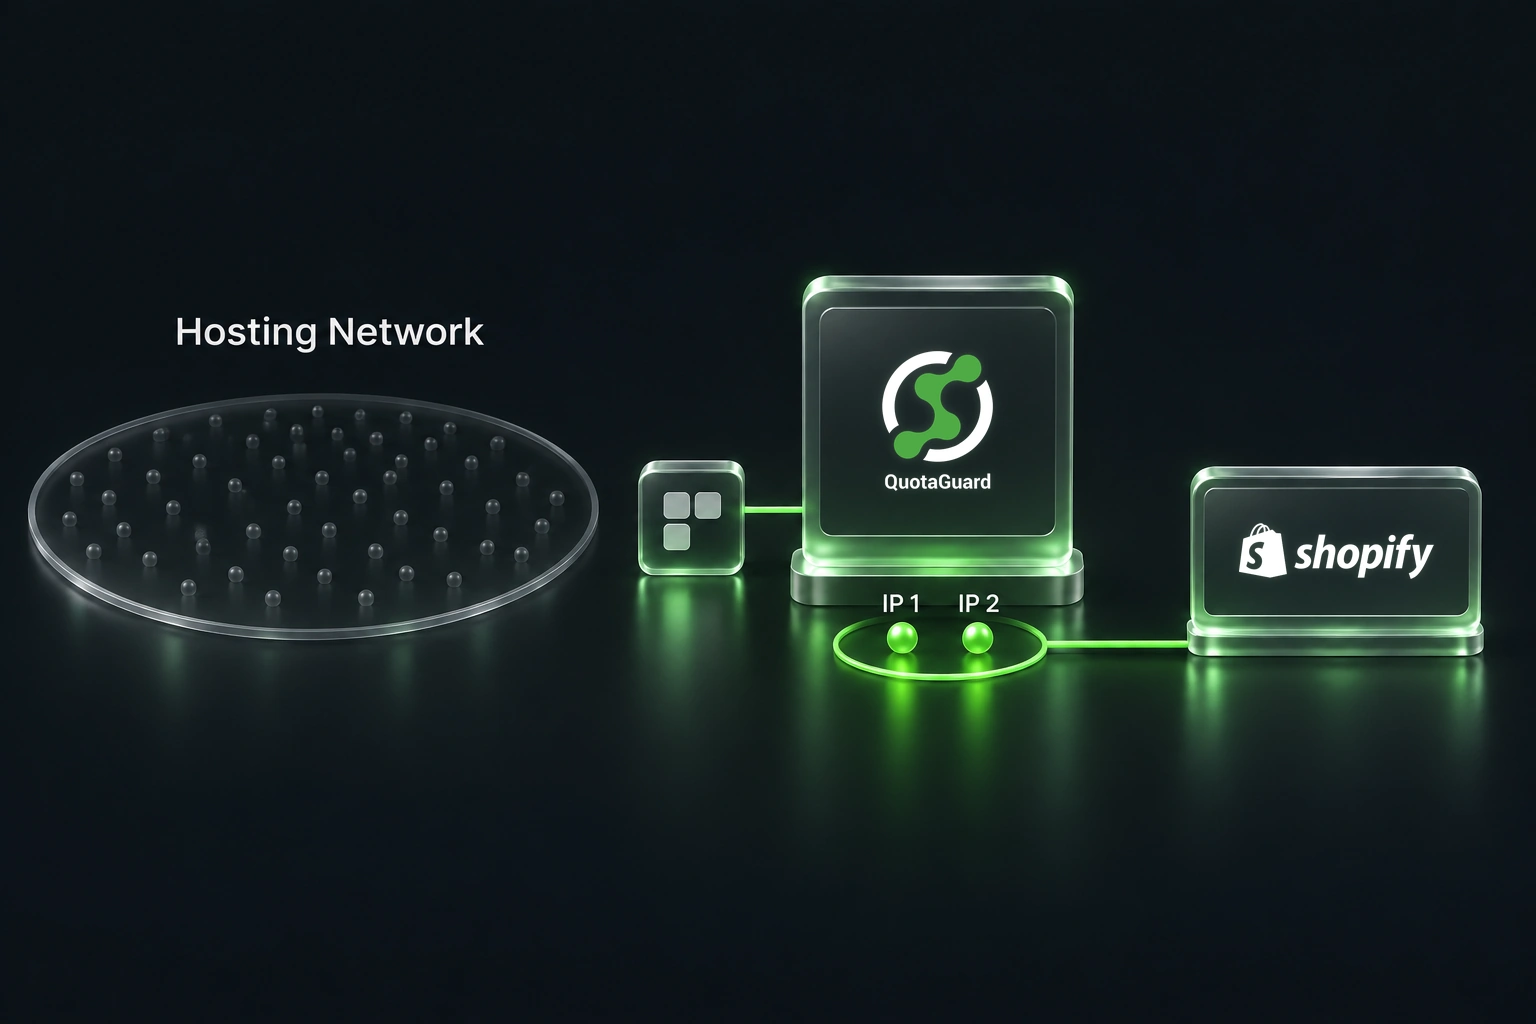
An Inbound Proxy works differently. It gives you a hostname that accepts a normal HTTPS request and forwards it to a configured destination:
NetSuite SuiteScript
        ↓ HTTPS request on port 443
QuotaGuard inbound hostname
        ↓ Request forwarded to the configured HTTPS site
WordPress REST endpoint
Although the feature is called an Inbound Proxy, it can serve this outbound SuiteScript use case. From NetSuite’s perspective, it is simply the HTTPS server being called. QuotaGuard handles the next connection to the actual website.
Support explained that the inbound proxy would forward requests from the subscription’s two dashboard IPs. After changing the Suitelet to use the inbound hostname, the customer confirmed that the integration worked.
Static does not mean exclusive. QuotaGuard’s Starter, Production and Business plans use shared static IP pairs; Enterprise plans are eligible for dedicated IPs and proxy resources; confirm with support that dedicated service has been provisioned for your subscription. A shared pair can satisfy a destination’s allowlist requirement, while a dedicated pair is the choice when the destination requires customer-exclusive source addresses. See the current plans for the distinction. Neither option guarantees acceptance by every host’s security filters, so verify the actual destination.
Set Up the Inbound Proxy and Update the Suitelet
QuotaGuard Static’s Inbound Proxy is included on direct plans starting with Starter, and on Heroku, AWS and Azure marketplace plans starting with Micro. The Inbound Proxy setup guide covers the dashboard screens.
- Open the correct subscription in the QuotaGuard dashboard. Select Inbound Proxy / Configure Inbound Proxies, then Create an Inbound Proxy.
- Set the forwarding URL to the real HTTPS website. Use the hostname the destination expects, including
wwwwhen appropriate. For example,https://www.example.com. - Choose the auto-generated QuotaGuard hostname. It will resemble
https://<your-hostname>.getstatica.com. This route avoids setting up a custom domain for the first test. - Update the Suitelet’s request URL. Replace the original site hostname with the generated hostname, retain the REST endpoint path, and use HTTPS without an explicit port. Remove the attempted
HostandProxy-Authorizationheaders. Keep the authentication the actual endpoint requires.
Configuration changes can take up to ten minutes to propagate.
Here is a shortened request inside an existing server-side SuiteScript that already imports N/https. The payload fields are examples; use the fields and authentication expected by your endpoint.
// Existing SuiteScript: `https` is the imported N/https module.
// Supply these values from your application's existing configuration.
// Keep secrets server-side; do not hard-code or log them.
var response = https.post({
    url: 'https://<your-hostname>.getstatica.com/wp-json/your-api/v1/endpoint',
    body: JSON.stringify({
        userid: userId,
        authkey: apiKey,
        mode: payload
    }),
    headers: {
        'Content-Type': 'application/json'
    }
});

// Apply your existing response handling here.
// Validate both response.code and the expected application response.
The example preserves the customer’s general JSON POST pattern without exposing their endpoint or credentials. The authkey field represents application authentication, not a QuotaGuard proxy password. If your endpoint uses a different authentication scheme, keep that scheme instead.
Oracle’s https.post reference documents the request parameters and JSON-stringification behavior.
Verify the Real Integration, Not Just Connectivity
Run an authorized test from the actual Suitelet against the intended endpoint. Check that:
- The response contains the expected API payload, not a hosting-provider challenge page. Check redirects too: a redirect to the original hostname can send a subsequent request outside the proxy route.
- The request reaches the intended REST path, with any required query parameters preserved through forwarding.
- The intended application operation succeeds. An HTTP success code alone does not prove that the integration completed its work.
- The destination operator can confirm the connection arrives from a QuotaGuard dashboard IP, using the connection source observed by the relevant server or security filter.
- If the destination uses an allowlist, both subscription IPs are included. Traffic can use either address; repeated requests do not guarantee that you have tested both paths.
- Requests without valid application authentication are still rejected.
NetSuite requires supported TLS and a trusted certificate chain for outbound HTTPS. If the new hostname produces a certificate error rather than an application response, check Oracle’s N/https requirements and the proxy configuration rather than disabling certificate verification.
Keep Application Authentication in Place
Anyone who knows the inbound hostname can send requests through it to the configured destination. Treat it as a reachable endpoint, not a secret authentication mechanism.
Keep the API key, signed token or other application-level check that protects the WordPress endpoint. Source-IP filtering and application authentication serve different purposes. This is especially important when a destination allows requests from the proxy addresses: that permission must not become permission for unauthenticated callers to perform application actions.
Use HTTPS for both the inbound URL and the configured forwarding URL. In this Static inbound arrangement, TLS terminates at the proxy, which makes a separate HTTPS connection to the origin. These are two encrypted connections, not one uninterrupted TLS session from NetSuite to WordPress. If your requirements depend on client certificates or end-to-end encryption through intermediaries, review the architecture with support before deployment. Do not assume a different proxy product is a drop-in replacement for this hostname-based setup.
Other Options and the Opposite Direction
The inbound-hostname pattern is a good fit for a fixed destination when you can change the SuiteScript request URL. It is not the only option:
- Destination-managed access: Oracle documents client-certificate authentication and DNS-based firewall rules as alternatives for outbound integrations. These depend on what the destination supports.
- A relay you control: If you need custom authentication, request transformation or routing logic before forwarding, a small hosted relay can make proxy-aware requests on the caller’s behalf. See static IPs for platforms without HTTP proxy support. Protect the relay and restrict its allowed destinations.
- Calls into NetSuite: If an application outside NetSuite is calling SuiteTalk or a RESTlet, that is the opposite direction. A proxy-capable application can use a forward proxy. Our NetSuite IP Address Rules article covers that scenario.
For SuiteScript calling a fixed external HTTPS endpoint, the useful lesson is simple: a client without a forward-proxy setting may still be able to use a normal HTTPS forwarding endpoint. In this case, changing the route restored the integration without trying to force proxy settings into N/https.
Start with the Inbound Proxy setup guide, or contact support@quotaguard.com with your caller, destination and observed error so we can help identify the right route.