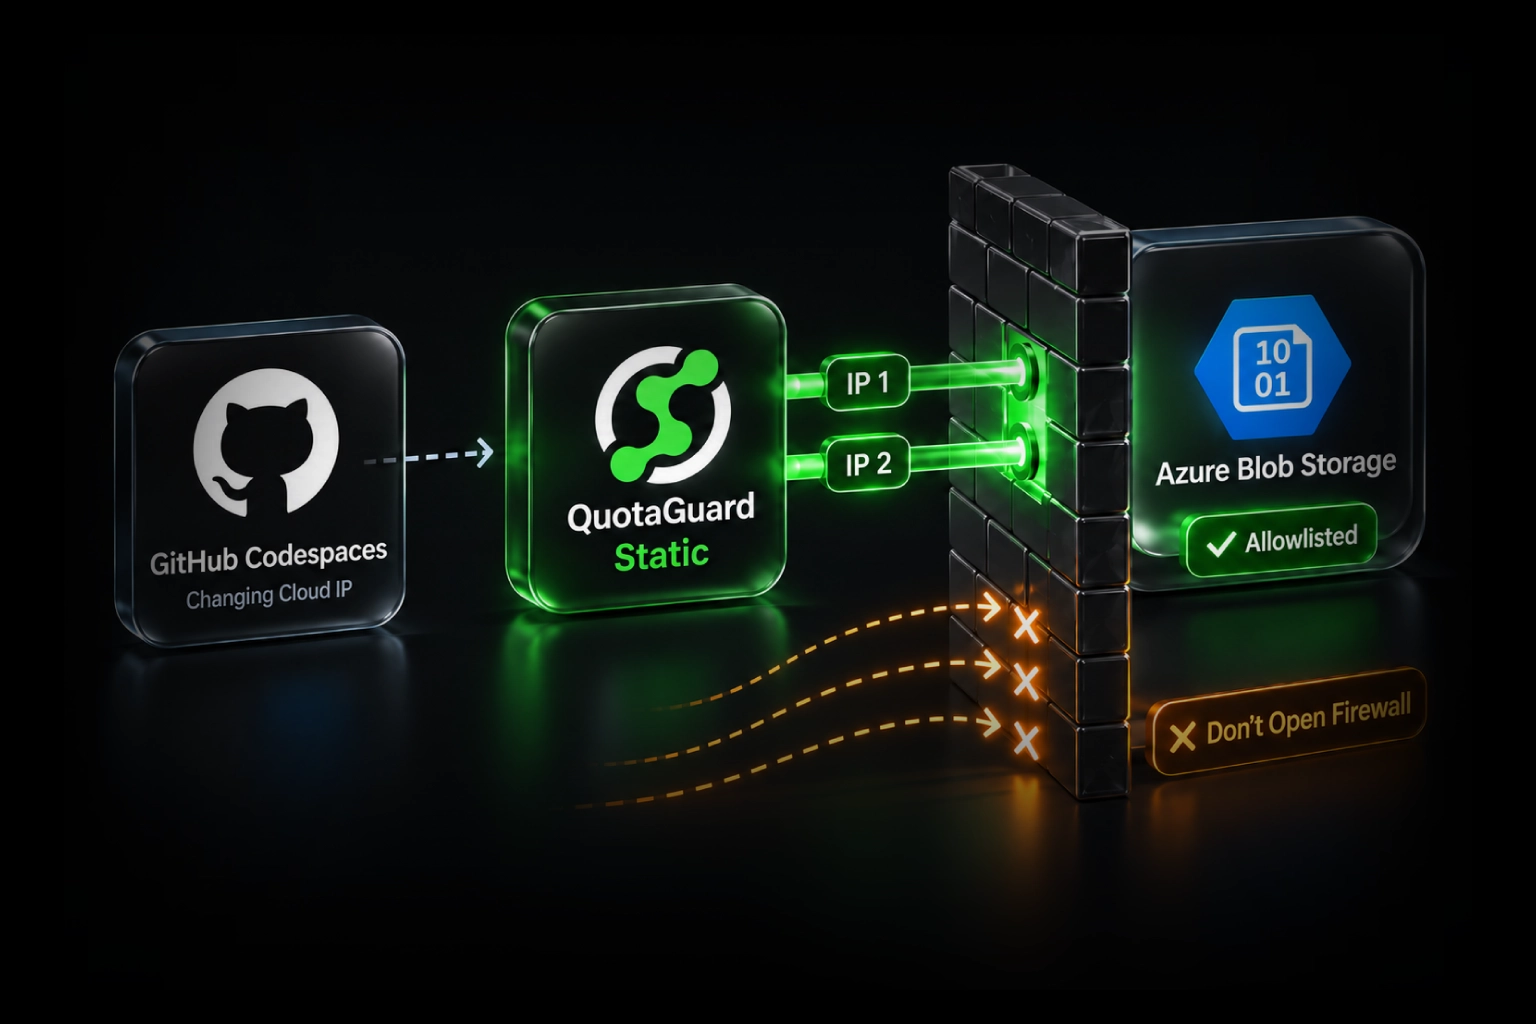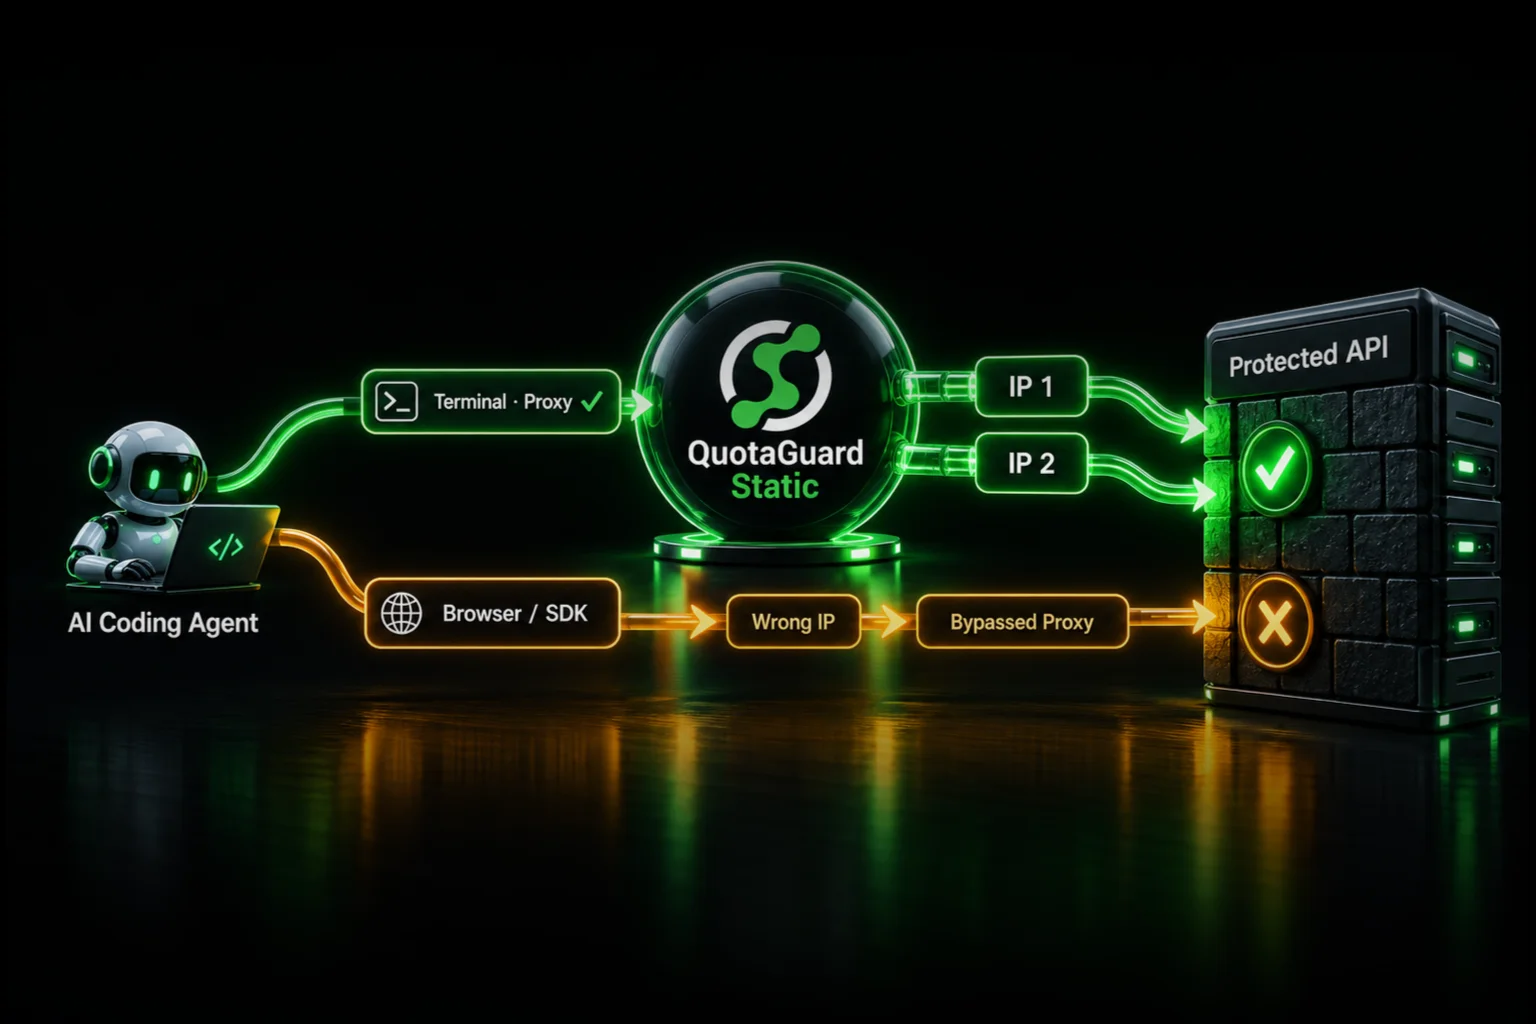
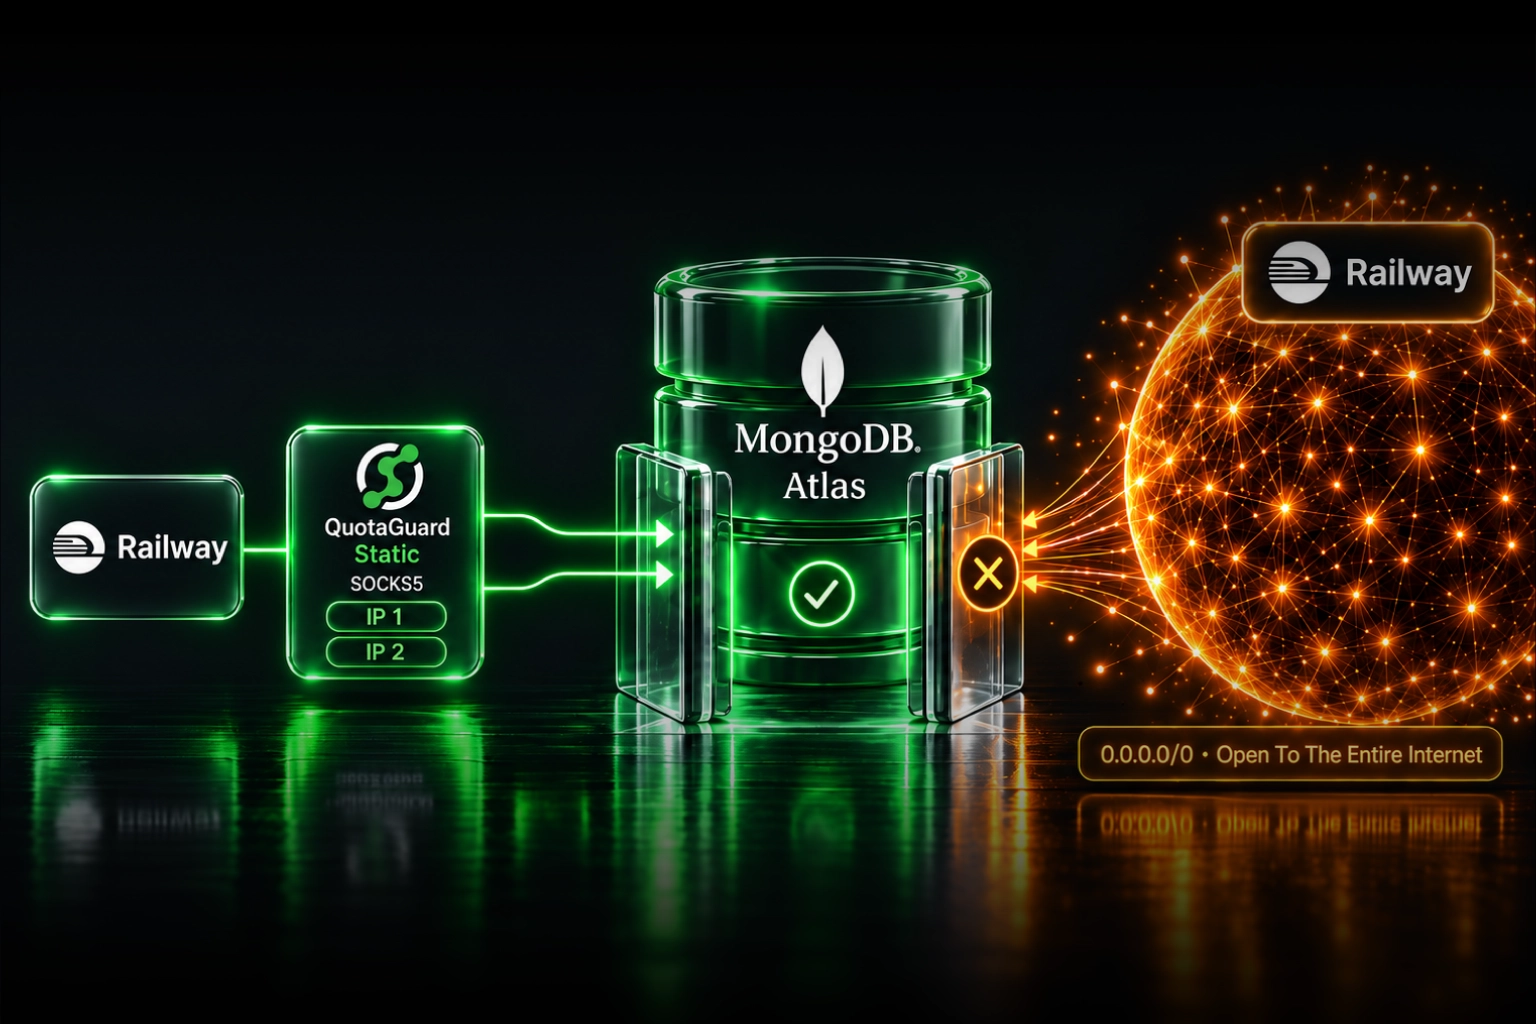
To connect a Railway application to MongoDB Atlas without opening the Atlas IP Access List to 0.0.0.0/0, route the native MongoDB client through QuotaGuard SOCKS5 or QGTunnel and add both QuotaGuard addresses to Atlas. The database keeps a narrow source-IP rule, while QuotaGuard operates the egress infrastructure, availability, failover, monitoring, capacity, and proxy incident response.
This is not an HTTP-proxy-only setup. MongoDB's wire protocol uses raw TCP, so setting HTTP_PROXY or HTTPS_PROXY on Railway does not prove that PyMongo, Motor, Mongoose, or another MongoDB driver uses QuotaGuard. Choose a driver with authenticated SOCKS5 support or run QGTunnel with the Railway service.
The resulting path is:
Railway service → QuotaGuard SOCKS5 or QGTunnel → Atlas IP Access List → MongoDB Atlas
A Railway developer demonstrated the exact problem
In September 2025, a developer asked Railway how a FastAPI backend could connect to MongoDB while keeping a specific-IP allowlist. The Hobby plan did not include Railway's native static egress feature. A moderator suggested either 0.0.0.0/0 or a regional Railway CIDR.
The developer rejected 0.0.0.0/0 because it would allow connection attempts from every IPv4 source. They also tested another hosting provider with a stable address, added that address to Atlas, and confirmed the connection worked. The problem was not whether the FastAPI application could use MongoDB. It was whether the application could present an identity Atlas could safely recognize.
The thread was ultimately resolved by allowlisting a Railway regional range. That can restore connectivity, but a cloud range is broader than the identity of one application and remains tied to Railway's published infrastructure. A managed two-address route provides a smaller, portable rule without asking the application team to operate its own proxy or NAT service.
What Atlas requires
MongoDB Atlas accepts client connections only from addresses or CIDR ranges in the project's IP Access List. MongoDB recommends using the smallest practical network segments and favoring individual addresses over large ranges.
The IP Access List is only one security layer. Keep all of the others:
- TLS for the connection to Atlas.
- A dedicated database user with a strong secret or approved workload identity.
- Least-privilege roles limited to the required database and operations.
- Secret rotation, audit logging, alerts, and backups.
Opening 0.0.0.0/0 does not turn those controls off, but it removes the source filter. Anyone holding a stolen credential can then attempt a connection from any IPv4 network instead of only through the approved application path.
Step 1: Create the QuotaGuard route
Create a QuotaGuard Static subscription in the region nearest the Railway service and Atlas deployment. The dashboard displays a proxy connection URL and two static outbound IP addresses. Standard plans use a stable pair on shared managed proxy infrastructure. If your policy requires exclusive customer-only addresses or isolated proxy resources, use a QuotaGuard Enterprise dedicated deployment.
Add the complete connection URL to the Railway service's Variables tab as:
QUOTAGUARDSTATIC_URL=http://username:password@<your-quotaguard-proxy-host>:9293Treat that value as a secret. Redeploy the service after adding or changing it. Do not print it in logs or commit it to the repository.
The HTTP-form connection URL is also what QGTunnel expects. QGTunnel uses the corresponding QuotaGuard SOCKS5 service for the TCP path. If a MongoDB driver supports SOCKS5 directly, use the SOCKS hostname, port 1080, username, and password shown for the same subscription.
Step 2: Add both addresses to Atlas
- Open the MongoDB Atlas project.
- Go to Security, then Network Access.
- Add the first QuotaGuard address as an individual IP entry.
- Add the second QuotaGuard address as another individual entry.
- Give both entries clear comments identifying the Railway application and QuotaGuard subscription.
Add both addresses because either proxy node may carry a connection. Leave any existing Railway range or temporary broad rule in place until the real application connection has succeeded through QuotaGuard. Removing the old entry first can create an avoidable outage.
Step 3A: Use QGTunnel for FastAPI and other drivers without a supported proxy setting
A Railway service runs in a Linux container, so it can launch QGTunnel before starting FastAPI. Add the QGTunnel package to the application image using the download and installation instructions in the QuotaGuard dashboard. The package includes the binary and the files required for transparent DNS mode.
In the dashboard, create the MongoDB tunnel configuration for the actual Atlas hosts and ports. A mongodb+srv:// address uses DNS discovery and can resolve to multiple Atlas hosts. Configure every discovered host required by the cluster rather than assuming that the visible cluster hostname is one TCP endpoint. Transparent mode preserves the hostnames used for Atlas TLS verification and replica-set discovery.
Prefix the Railway start command with QGTunnel. For a typical FastAPI service, that shape is:
bin/qgtunnel uvicorn main:app --host 0.0.0.0 --port "$PORT"Replace main:app with the application's real module and object. Keep the normal Atlas connection string in the application, including its TLS and authentication settings. QGTunnel starts the configured local routes and then launches Uvicorn.
MongoDB topology can change when Atlas maintenance, scaling, or configuration changes introduce different hosts. If the cluster uses SRV discovery, review the resolved host set during setup and whenever Atlas changes the deployment. QuotaGuard support can help map the connection string to the required tunnel configuration.
Step 3B: Prefer driver-native SOCKS5 when the MongoDB driver supports it
Several current MongoDB drivers expose SOCKS5 settings. Driver-native configuration avoids a separate tunnel process and keeps the proxy scoped to the MongoDB client. Follow the documentation for the exact language and installed driver version.
For example, the current MongoDB Node.js driver supports proxyHost, proxyPort, proxyUsername, and proxyPassword. It also requires the optional socks package:
npm install mongodb socksimport { MongoClient } from "mongodb";
const client = new MongoClient(process.env.MONGODB_URI, {
proxyHost: process.env.QUOTAGUARD_SOCKS_HOST,
proxyPort: 1080,
proxyUsername: process.env.QUOTAGUARD_SOCKS_USER,
proxyPassword: process.env.QUOTAGUARD_SOCKS_PASSWORD,
});
await client.connect();
await client.db("admin").command({ ping: 1 });Add those four QuotaGuard values as Railway secret variables. Do not assume that this JavaScript example applies to PyMongo, Motor, Mongoose, or an older Node.js driver. Use the documented proxy interface for the actual client, and use QGTunnel when the client does not expose a compatible authenticated SOCKS5 route.
Step 4: Verify the database connection, not a separate web request
A successful request to an IP-reflection website proves only that the HTTP request used the proxy. It does not prove that a native MongoDB connection followed the same path.
Deploy the Railway service and run a real Atlas operation such as a driver ping, health check, or small read. Then inspect the Railway and Atlas connection evidence:
- QGTunnel or the MongoDB driver starts without proxy-authentication errors.
- DNS discovery resolves every required Atlas host.
- TLS hostname verification succeeds.
- Atlas accepts the connection while only the two QuotaGuard addresses and any temporary migration entries are approved.
- Connection pooling, reconnects, background workers, and every production replica continue working.
After the routed database connection is stable, remove 0.0.0.0/0 or the broad Railway range. MongoDB notes that connections from a removed address may remain open for a variable period, so test a new connection after the rule change instead of treating an existing pooled socket as proof.
Why not just use Railway's native static outbound IPs?
Railway Pro currently provides three permanent outbound IPv4 addresses per service and load balances traffic across them. Railway specifically lists MongoDB Atlas as a use case. The addresses are not guaranteed to be dedicated, and they change if the service moves to a different Railway region.
That feature is appropriate when the team already wants Railway Pro and prefers service-wide, platform-managed egress. QuotaGuard is the normal choice when the application can insert a SOCKS5 or QGTunnel route and values:
- A smaller two-address rule: approve the QuotaGuard pair rather than a regional cloud range.
- Portability: keep the Atlas allowlist if the application changes Railway regions or moves to another hosting platform.
- Selective routing: route the MongoDB client through QuotaGuard without changing unrelated application traffic.
- Managed operations: QuotaGuard operates the proxy nodes, failover, monitoring, capacity, maintenance, and proxy incident response.
- Engineer support: get help mapping the application's actual driver and Atlas topology instead of owning a homegrown proxy alone.
The decision is not a one-dollar comparison between old plan prices mentioned in a community thread. It is which network identity fits the architecture and who should own the infrastructure behind it.
Troubleshooting Railway to Atlas
The connection times out after adding the QuotaGuard addresses. The database client probably is not using the SOCKS5 or QGTunnel path, or the tunnel is missing one of the Atlas hosts. Adding an address to Atlas does not reroute traffic by itself.
The service reports an SSL handshake error. Do not immediately disable TLS validation. Confirm that transparent mode preserves the Atlas hostname, that every SRV-discovered host is configured, that the system clock and CA bundle are current, and that the connection reaches an allowlisted source.
It worked until Atlas maintenance or scaling. Re-resolve the SRV record and compare the current Atlas host set with the QGTunnel configuration. Add newly introduced destinations and redeploy.
Only one QuotaGuard address appears. That is normal during a short test. Both addresses must remain allowlisted because load balancing and failover can use either one.
Railway variables are present but MongoDB still uses Railway egress. Environment variables do not redirect raw TCP automatically. Configure the driver explicitly or make QGTunnel the parent process in the Railway start command.
QuotaGuard Static or Shield?
QuotaGuard Static starts at $19 per month and is the normal starting point for Atlas allowlisting. MongoDB's TLS session continues to protect the database payload to Atlas; QuotaGuard's blind SOCKS or tunnel path does not decrypt that payload. The Static client-to-proxy SOCKS connection is not separately wrapped in TLS.
QuotaGuard Shield starts at $29 per month and adds TLS protection to the customer-to-proxy hop through its supported secure connection methods. It is not a drop-in replacement for every direct SOCKS5 driver configuration. Choose Shield when the approved security architecture requires that protected first hop, and confirm the driver or tunnel method supports the intended Shield route.
Official references and direct evidence
Railway developer: FastAPI to MongoDB without 0.0.0.0/0
MongoDB Atlas: Configure IP Access List Entries
MongoDB Atlas: Network Security Guidance
MongoDB Node.js driver: Enable SOCKS5 Proxy Support
Related QuotaGuard guides
QuotaGuard and Railway Integration Guide
QuotaGuard and MongoDB Atlas Integration Guide
Why Developers Open Databases to 0.0.0.0/0 When Cloud Egress Keeps Changing
Keep Railway and keep the narrow Atlas rule
A dynamic Railway address does not require an internet-wide Atlas entry or a broad regional trust boundary. Put the native MongoDB connection on a supported SOCKS5 or QGTunnel path, approve both QuotaGuard addresses, verify the actual driver connection, and then remove the temporary broad rule.
Start a QuotaGuard Static trial, or contact QuotaGuard support with the Railway start command, language, MongoDB driver and version, and redacted Atlas hostname. We will help determine whether driver-native SOCKS5 or QGTunnel is the better route.