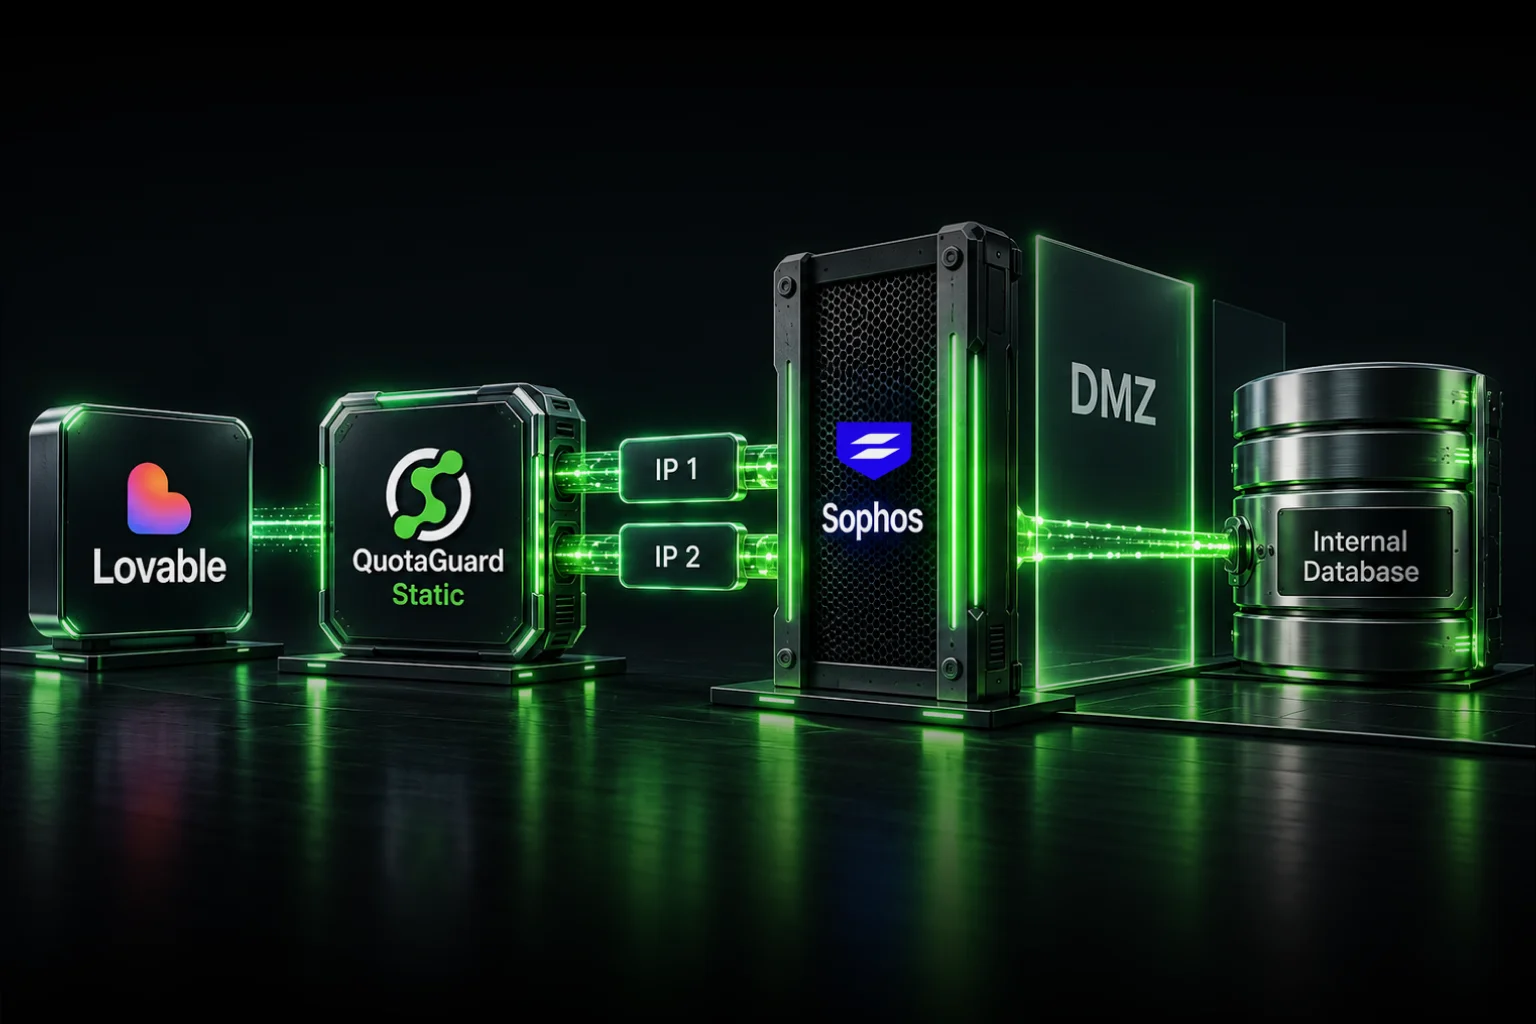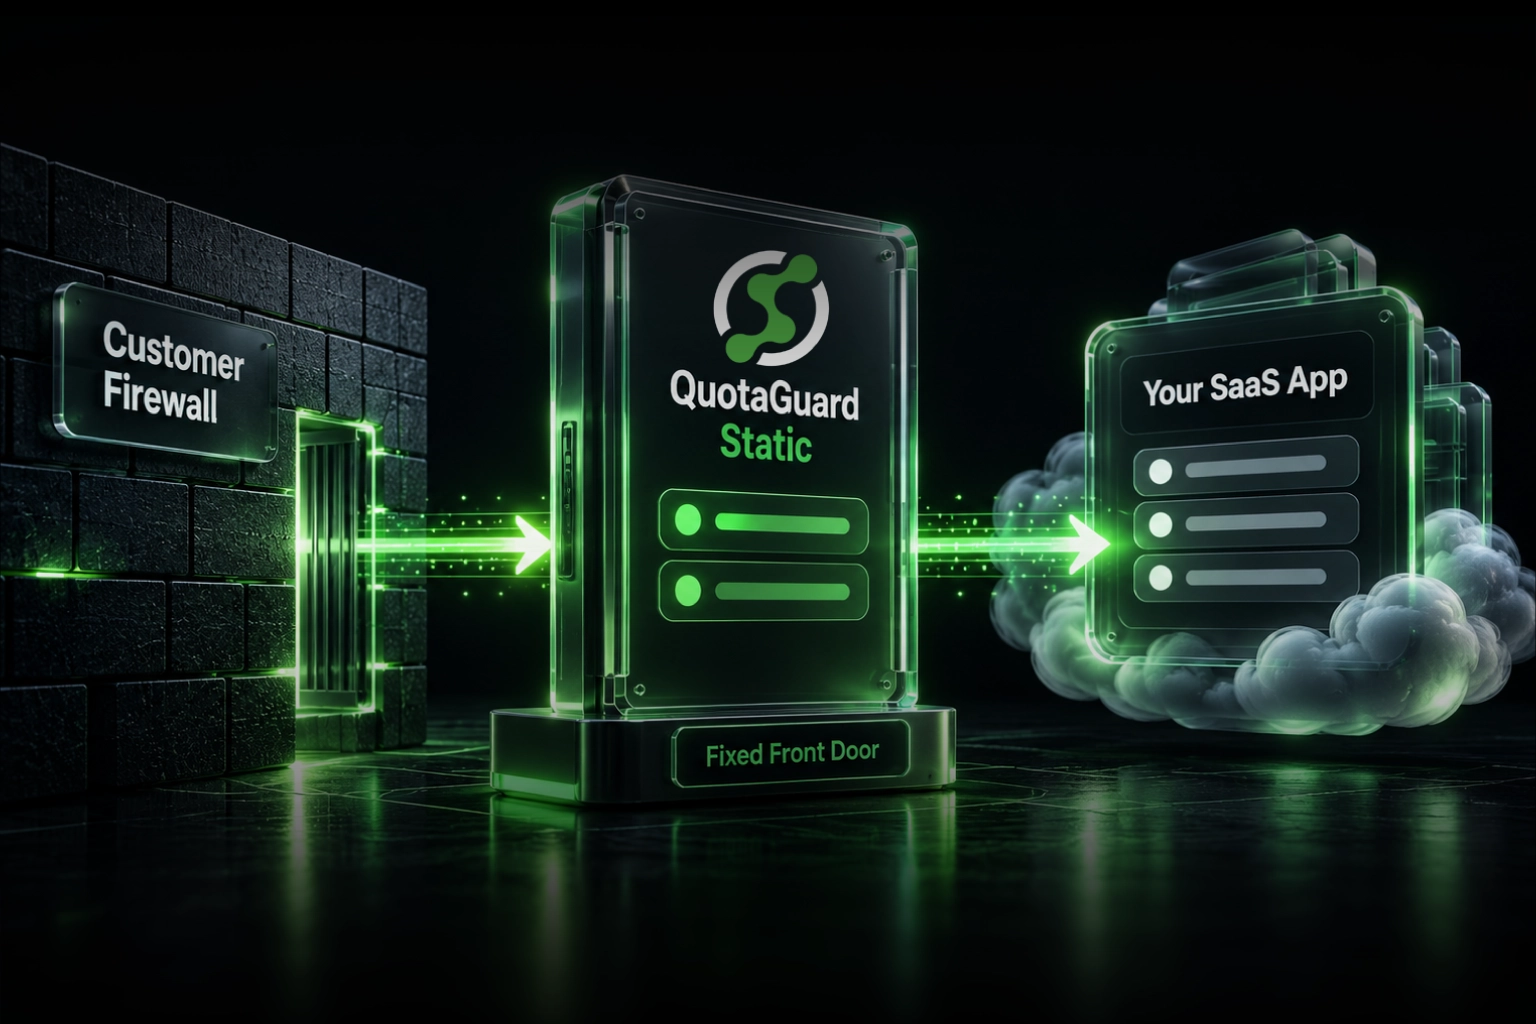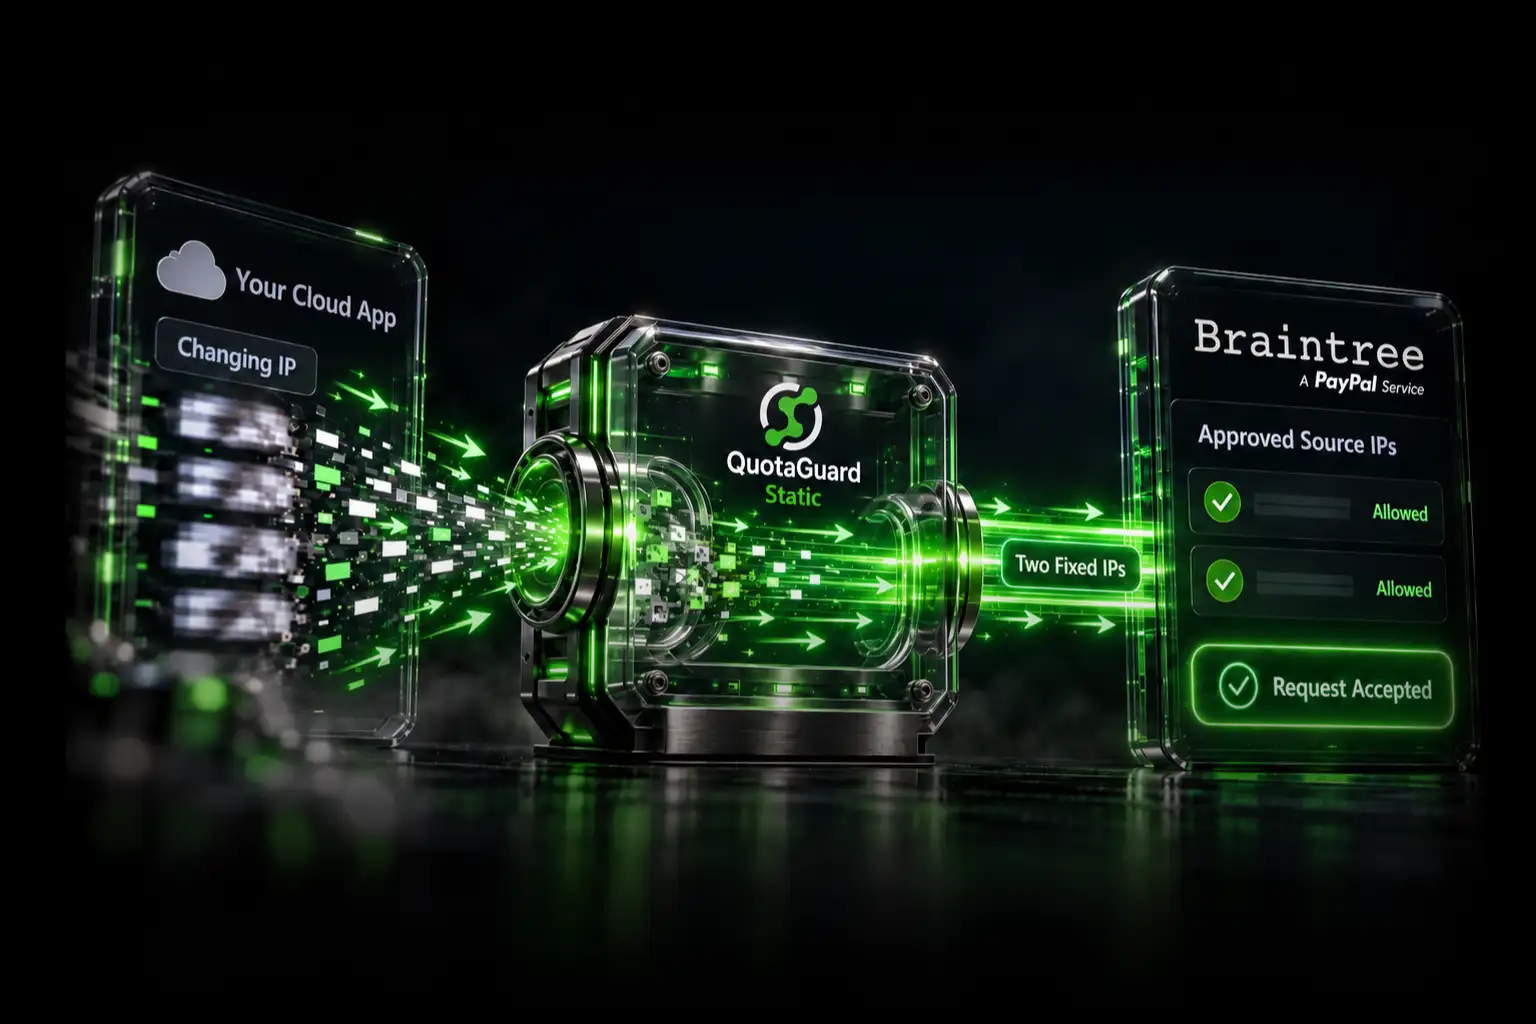

Render's 2025 outbound-IP migration demonstrated why production allowlists should not depend on a hosting platform's changing shared ranges. QuotaGuard gives a Render application two stable outbound addresses and keeps the protected connection independent of those platform changes.
Render maintains first-party QuotaGuard setup documentation. Configure the API, database, payment-provider, or partner connection to use QuotaGuard, give the destination both subscription IPs, and the destination continues to see that stable pair when Render changes its ordinary infrastructure.
This is not only about avoiding an emergency firewall edit. QuotaGuard operates the proxy infrastructure, load balancing, health checks, failover, monitoring, capacity, and incident response. Your team gets a stable egress service without building another production network component it must maintain.
What Happened in 2025
On September 24, 2025, Render announced that new outbound IP ranges would begin rolling out in every region on October 27, 2025. Render also said each region's original outbound addresses would be retired no later than December 1, 2025.
Those dates are now historical, but the operational lesson remains current. A team using Render's shared ranges had to identify every downstream allowlist, add the new ranges before traffic moved, and later remove the retired entries.
When a client or vendor controls the firewall, that change can require a ticket, a security review, testing, and coordination across organizations. A normal hosting-platform migration can therefore become an application outage even when the application code never changed.
Decouple the Application Identity from Render's Shared Ranges
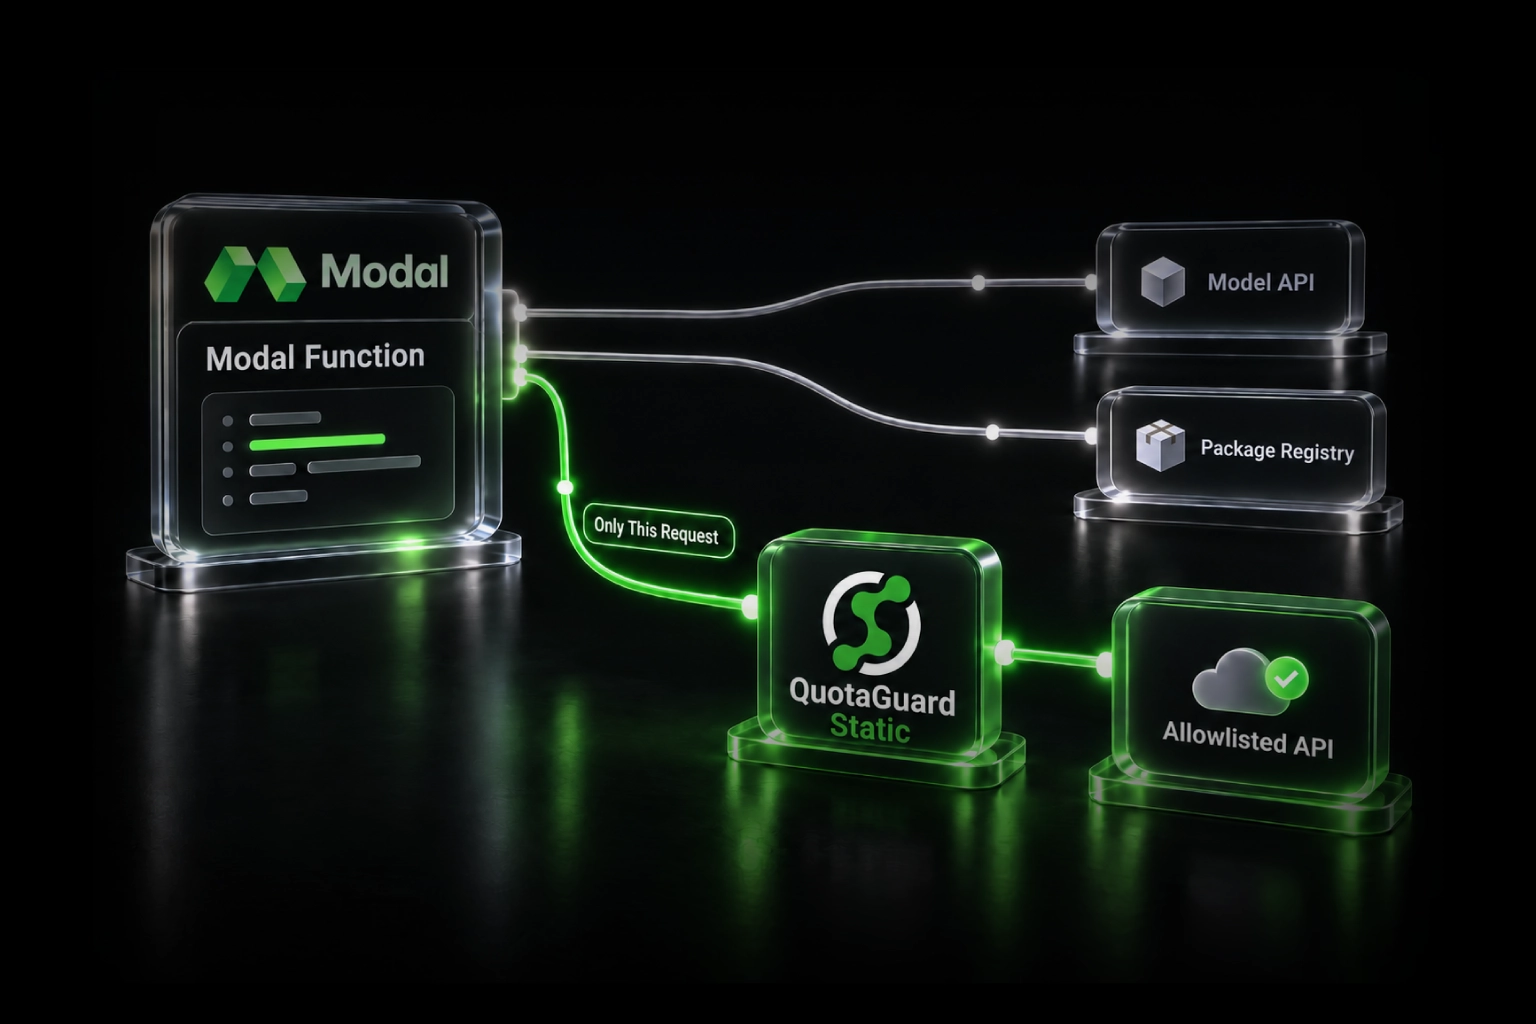
Render application → QuotaGuard → allowlisted destination
When the protected connection uses QuotaGuard, the destination evaluates the QuotaGuard source address rather than Render's ordinary shared egress. The allowlist belongs to the integration instead of the temporary shape of the hosting platform.
- Stable pair: the destination approves both addresses displayed in the QuotaGuard subscription.
- Selective route: only clients and destinations configured for QuotaGuard use the proxy or tunnel.
- Managed availability: QuotaGuard operates health checks, load balancing, failover, monitoring, capacity, and incident response.
- Fewer firewall projects: routine Render infrastructure changes no longer require changing the allowlist for that configured connection.
- Portable identity: the same route can remain in place if the workload later moves away from Render.
- Direct support: QuotaGuard engineers can help identify the right HTTP, SOCKS5, or QGTunnel path.
QuotaGuard Static starts at $19 per month. The stronger reason to use it is operational: QuotaGuard owns the egress infrastructure and the pages when that infrastructure needs attention.
Configure and Verify the Route
- Create a QuotaGuard subscription in the region nearest the Render service.
- Store the authenticated proxy URL as
QUOTAGUARDSTATIC_URLin the service's secret environment variables or a Render environment group. - Configure the exact application client that connects to the protected destination.
- Ask the destination to allowlist both QuotaGuard addresses.
- Send a request through the configured client to
https://ip.quotaguard.com. - Confirm the result matches an address in the QuotaGuard dashboard before removing the previous firewall entries.
Adding the environment variable does not redirect traffic automatically. The application client must be configured to use it. HTTP and HTTPS libraries can use the authenticated proxy when they support an explicit proxy or compatible dispatcher.
Databases, SFTP, Redis, and other raw TCP protocols do not automatically inherit an HTTP proxy setting. Use a compatible SOCKS5 client or QGTunnel. The complete instructions are in How to Get a Static IP for Render Apps.
Plan an Allowlist Migration Without an Outage
- Inventory the dependencies. Identify every external system that authorizes the application by source IP and record who controls each firewall.
- Add both QuotaGuard addresses first. Keep the previous route approved during the validation window when the destination permits overlap.
- Test the production client. A separate IP-echo test is useful, but it does not prove a different API or database client uses the same route.
- Observe the cutover. Confirm successful requests, timeouts, latency, and the source address recorded by the destination.
- Remove obsolete access. Once the QuotaGuard path is stable, remove old ranges that are no longer needed.
A Short Disclosure About Render Dedicated IPs
Render also sells native dedicated outbound IP sets. The feature requires a Pro workspace or higher, costs $100 per regional set each month, provides three exclusive IPv4 addresses, and applies to an entire workspace or selected environments in one Render region. The identity remains tied to Render.
That option is relevant when a policy specifically requires customer-exclusive addresses and transparent platform-level routing for all supported traffic in scope. For the common case where selected external systems need a small stable allowlist, QuotaGuard provides the targeted managed route. QuotaGuard Enterprise is available when the QuotaGuard deployment itself must use exclusive IPs and proxy resources.
Address ownership: QuotaGuard Starter, Production, and Business plans provide a stable pair on managed shared proxy infrastructure. The addresses are stable for allowlisting but are not customer-exclusive.
Stop Turning Hosting Changes into Firewall Emergencies
Render's 2025 migration was a visible example of a recurring cloud problem: shared infrastructure changes, while client and vendor firewalls expect a stable caller.
QuotaGuard separates those concerns. Render continues running the application. QuotaGuard provides the stable managed egress identity. The destination keeps a small allowlist that is not coupled to Render's ordinary regional ranges.
View QuotaGuard plans or talk directly to a QuotaGuard engineer about the destination and protocol you need to protect.